 listicle
7 Ways to Improve Data Security in Burbank Offices
Table of Contents
- 1. Enforce Strong Password Management and Multi-Factor Authentication
- 2. Deploy Managed Cybersecurity Services in Burbank
- 3. Implement AI-Driven Threat Detection Tools
- 4. Establish CCPA Compliance for Burbank Businesses
- 5. Automate Backups and Ransomware Recovery
- 6. Conduct Regular Security Awareness Training
- 7. Secure Physical and Digital Document Disposal
- Frequently Asked Questions
Last Updated: September 20, 2026
Data breaches in California offices are accelerating. The average enterprise now faces three to four significant security incidents annually. For organizations in the Los Angeles area managing sensitive customer data, employee records, or financial information, the stakes couldn't be higher.
This guide covers 7 ways to improve data security in Burbank offices, concrete steps your team can implement immediately to reduce breach risk, meet compliance requirements, and protect critical assets. Physical safeguards remain a vital component of this strategy, as upgrading office security systems ensures that unauthorized personnel cannot gain the access necessary to compromise sensitive digital infrastructure.
1. Enforce Strong Password Management and Multi-Factor Authentication
Weak passwords and password reuse remain the leading cause of unauthorized access. A single compromised credential gives attackers a foothold into your entire network. Enforce strong, unique passwords across all systems and require multi-factor authentication (MFA) for critical applications.
What strong password enforcement looks like:
Start with a centralized password manager. Tools like Bitwarden's password management solution provide encrypted vaults where employees store login credentials securely. This eliminates the need to memorize complex passwords or write them on sticky notes. Bitwarden offers free and paid tiers starting at $3 per user per month, making it accessible for offices of any size.
Next, layer in multi-factor authentication. Duo Security's MFA platform verifies user identity through a second method, typically a push notification to a mobile device, before granting access. This stops attackers cold, even if they've stolen a password. Duo Security also starts at $3 per user per month and integrates with most enterprise applications.
Implementation steps:
- Deploy a password manager company-wide and mandate its use
- Enable MFA on email, cloud storage, and VPN access first
- Require MFA for any account with administrative privileges
- Set password policies: minimum 14 characters, complexity requirements, 90-day rotation
2. Deploy Managed Cybersecurity Services in Burbank
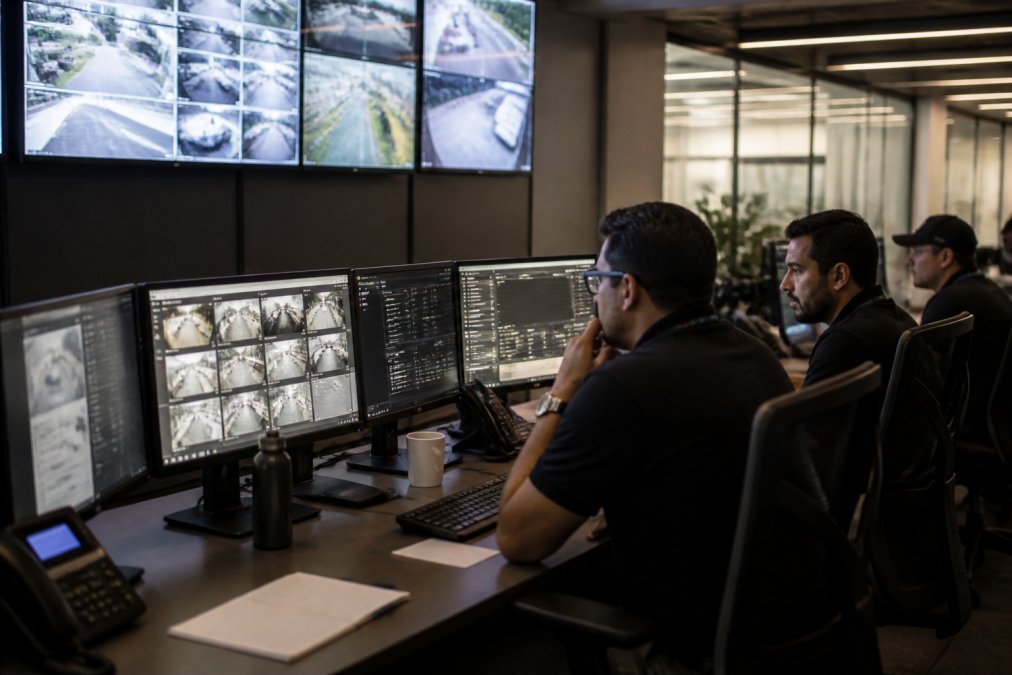
Most offices lack the in-house expertise to monitor threats 24/7. A single missed alert can turn into a full-scale breach. This is where managed cybersecurity services become essential.
What managed services include:
A managed cybersecurity provider monitors your network traffic, endpoint activity, and log files continuously, identifying suspicious behavior and escalating genuine threats for immediate action. VegaNext delivers enterprise-grade cybersecurity through AI-native managed detection and response, combining automated threat detection with expert analysis to reduce false positives.
Managed services can provide deeper expertise.
Key capabilities to require:
- 24/7 threat monitoring and detection
- Rapid incident response and containment
- Integration with your existing tools and infrastructure
- Compliance reporting for regulatory requirements
- Regular security assessments and recommendations
When evaluating managed cybersecurity services, prioritize providers who understand your specific industry and regulatory environment, HIPAA for healthcare, PCI-DSS for financial services, vendor risk management for supply chain.
3. Implement AI-Driven Threat Detection Tools
Traditional rule-based security tools generate alert fatigue, hundreds of daily notifications, most false positives. AI-driven threat detection identifies patterns humans would miss and prioritizes alerts based on actual risk, reducing false positives while catching sophisticated attacks.
How AI threat detection works:
AI models analyze network traffic, endpoint behavior, and user activity patterns to learn what "normal" looks like for your organization. When behavior deviates significantly from the baseline, the system flags it for investigation.
Unlike rule-based systems, AI models detect novel attack patterns and behavioral anomalies that indicate ransomware activity, even without a known signature.
Practical implementation:
Start by collecting baseline data. Deploy AI detection tools in monitoring mode for 2-4 weeks. Let the system learn your normal operations. Then activate enforcement mode, where the tool actively blocks or alerts on suspicious activity.
For offices with hybrid workforces, AI detection is particularly valuable. AI models understand context, a remote employee logging in from home at 9 PM is normal; the same employee logging in from five different countries in one hour is suspicious.
Integration with your existing infrastructure:
AI threat detection works best when integrated with your SIEM (Security Information and Event Management) system, endpoint protection platform, and incident response workflows to create a cohesive security architecture.
4. Establish CCPA Compliance for Burbank Businesses
California's Consumer Privacy Act (CCPA) applies to any business collecting personal information from California residents. CCPA compliance establishes data governance practices that protect your organization and build customer trust.
Core CCPA requirements:
The CCPA grants California residents four rights: the right to know what personal information is collected, the right to delete personal information, the right to opt out of data sales, and the right to non-discrimination for exercising these rights.
Your organization must:
- Disclose what personal information you collect and how you use it
- Provide mechanisms for consumers to request data access, deletion, and opt-out
- Honor these requests within 45 days
- Maintain records of consumer requests and your responses
- Conduct privacy impact assessments for new data processing activities
Practical compliance steps:
Conduct a data inventory documenting all personal information collected, names, email addresses, phone numbers, purchase history, browsing behavior. Identify where data flows, retention periods, and third-party sharing.
Update your privacy policy. Make it clear, specific, and easy to understand. Explain what data you collect, why you collect it, how long you keep it, and who you share it with. Include instructions for consumers to exercise their rights.
Implement processes to handle consumer requests for data access, deletion, and opt-out within 45 days. This requires coordination across IT, customer service, marketing, and finance.
Vendor management:
5. Automate Backups and Ransomware Recovery
Ransomware attacks encrypt your files and demand payment for decryption. Automated backup systems ensure you can recover without negotiating with criminals.
Backup fundamentals:
Ransomware-specific protection:
Recovery testing:
6. Conduct Regular Security Awareness Training
Your team is your first line of defense against social engineering, phishing, and credential theft. Security awareness training reduces human risk by teaching employees to recognize and avoid attacks.
What effective training covers:
- Phishing email recognition: How to spot fake emails impersonating trusted senders
- Password security: Why strong, unique passwords matter and how to use password managers
- Physical security: Protecting devices from theft, securing documents, preventing tailgating
- Social engineering: Recognizing manipulation tactics and verification procedures
- Incident reporting: How to report suspicious activity without fear of punishment
- Compliance requirements: CCPA, HIPAA, or other regulations relevant to your industry
Making training stick:
Measuring effectiveness:
7. Secure Physical and Digital Document Disposal
Sensitive documents often end up in office trash where attackers can find them. Deleted files can be recovered from hard drives without proper wiping.
Physical document disposal:
Digital document disposal:
When retiring computers, hard drives, or other storage devices:
- Use secure data wiping software that overwrites all data multiple times
- For highly sensitive data, physically destroy the storage device
- Document the disposal process for compliance records
Hybrid considerations:
| Strategy | Primary Benefit | Implementation Timeline |
|---|---|---|
| Strong authentication | Prevents credential-based attacks | 2-4 weeks |
| Managed cybersecurity | 24/7 threat detection and response | 4-8 weeks |
| AI threat detection | Reduces false positives, catches novel threats | 6-12 weeks |
| CCPA compliance | Legal compliance, customer trust | 8-12 weeks |
| Automated backups | Ransomware recovery, business continuity | 1-2 weeks |
| Security awareness training | Reduces human error and social engineering | Ongoing |
| Document disposal | Eliminates physical data breach risk | 2-4 weeks |
Frequently Asked Questions
What are the most common cybersecurity threats for businesses in Burbank?
Burbank offices face phishing attacks, ransomware, credential theft, and insider threats. Phishing remains the leading attack vector, exploiting human error to gain access to sensitive data. Ransomware targeting healthcare and financial services can halt operations entirely. Credential compromise through weak passwords or reused logins enables unauthorized access. Implementing strong password management, MFA, security training, and managed cybersecurity services significantly reduces exposure to these threats.
How does a Managed Service Provider improve data security for Burbank offices?
A Managed Service Provider offers 24/7 monitoring, threat detection, and incident response without requiring a dedicated internal security team. MSPs deploy enterprise-grade tools, manage patches and updates, conduct vulnerability assessments, and handle compliance requirements. For Burbank businesses with limited IT budgets, managed cybersecurity services provide expert-level protection, faster threat response, and reduced operational burden, allowing your team to focus on core business functions.
What California state laws govern data privacy for Burbank businesses?
The California Consumer Privacy Act (CCPA) and California Privacy Rights Act (CPRA) are the primary regulations affecting Burbank businesses. CCPA requires businesses to disclose data collection practices, allow consumer opt-outs, and implement reasonable security measures. CPRA, effective 2023, expands consumer rights and increases penalties for non-compliance. Burbank offices handling California resident data must establish CCPA compliance programs, conduct privacy impact assessments, and maintain audit trails to demonstrate compliance.
How can AI-native security solutions protect Burbank office networks?
AI-driven threat detection tools analyze network traffic, user behavior, and system logs in real-time to identify anomalies and threats faster than manual monitoring. AI automation reduces false positives, enabling security teams to focus on genuine threats. AI-native solutions detect zero-day vulnerabilities, predict attack patterns, and respond to incidents automatically. For Burbank enterprises managing complex hybrid infrastructure, AI-driven threat detection provides continuous protection and faster incident containment.